Youngstown Local Index
Local routes.
Burning River Cyber Con 2026 convened on Saturday, November 14, 2026, at 78th Street Studios in Cleveland, Ohio, bringing practitioners, security leaders and technology professionals from across Northeast Ohio and the broader Rust Belt together for a full day of technical sessions, candid discussion and professional networking. Presented under the theme “Deja New,” the 2026 program marked the second edition of a conference that organizers describe as “Igniting Cyber Security in the Heart of the Rust Belt.”
For business owners, IT managers and security teams in Youngstown and the Mahoning Valley, the event offered a concentrated, regional view of where attackers are investing their effort and where defenders are finding measurable results, all within a short drive of home.
Event Overview
- Event: Burning River Cyber Con 2026, “Deja New” (second annual edition)
- Date: Saturday, November 14, 2026
- Hours: 9:00 AM to 5:00 PM, followed by an evening reception
- Venue: 78th Street Studios, Cleveland, Ohio
- Audience: Penetration testers, red teamers, security analysts, incident responders, CISOs and IT leaders
- Official website: BurningRiverCyberCon.com
A Practitioner’s Forum
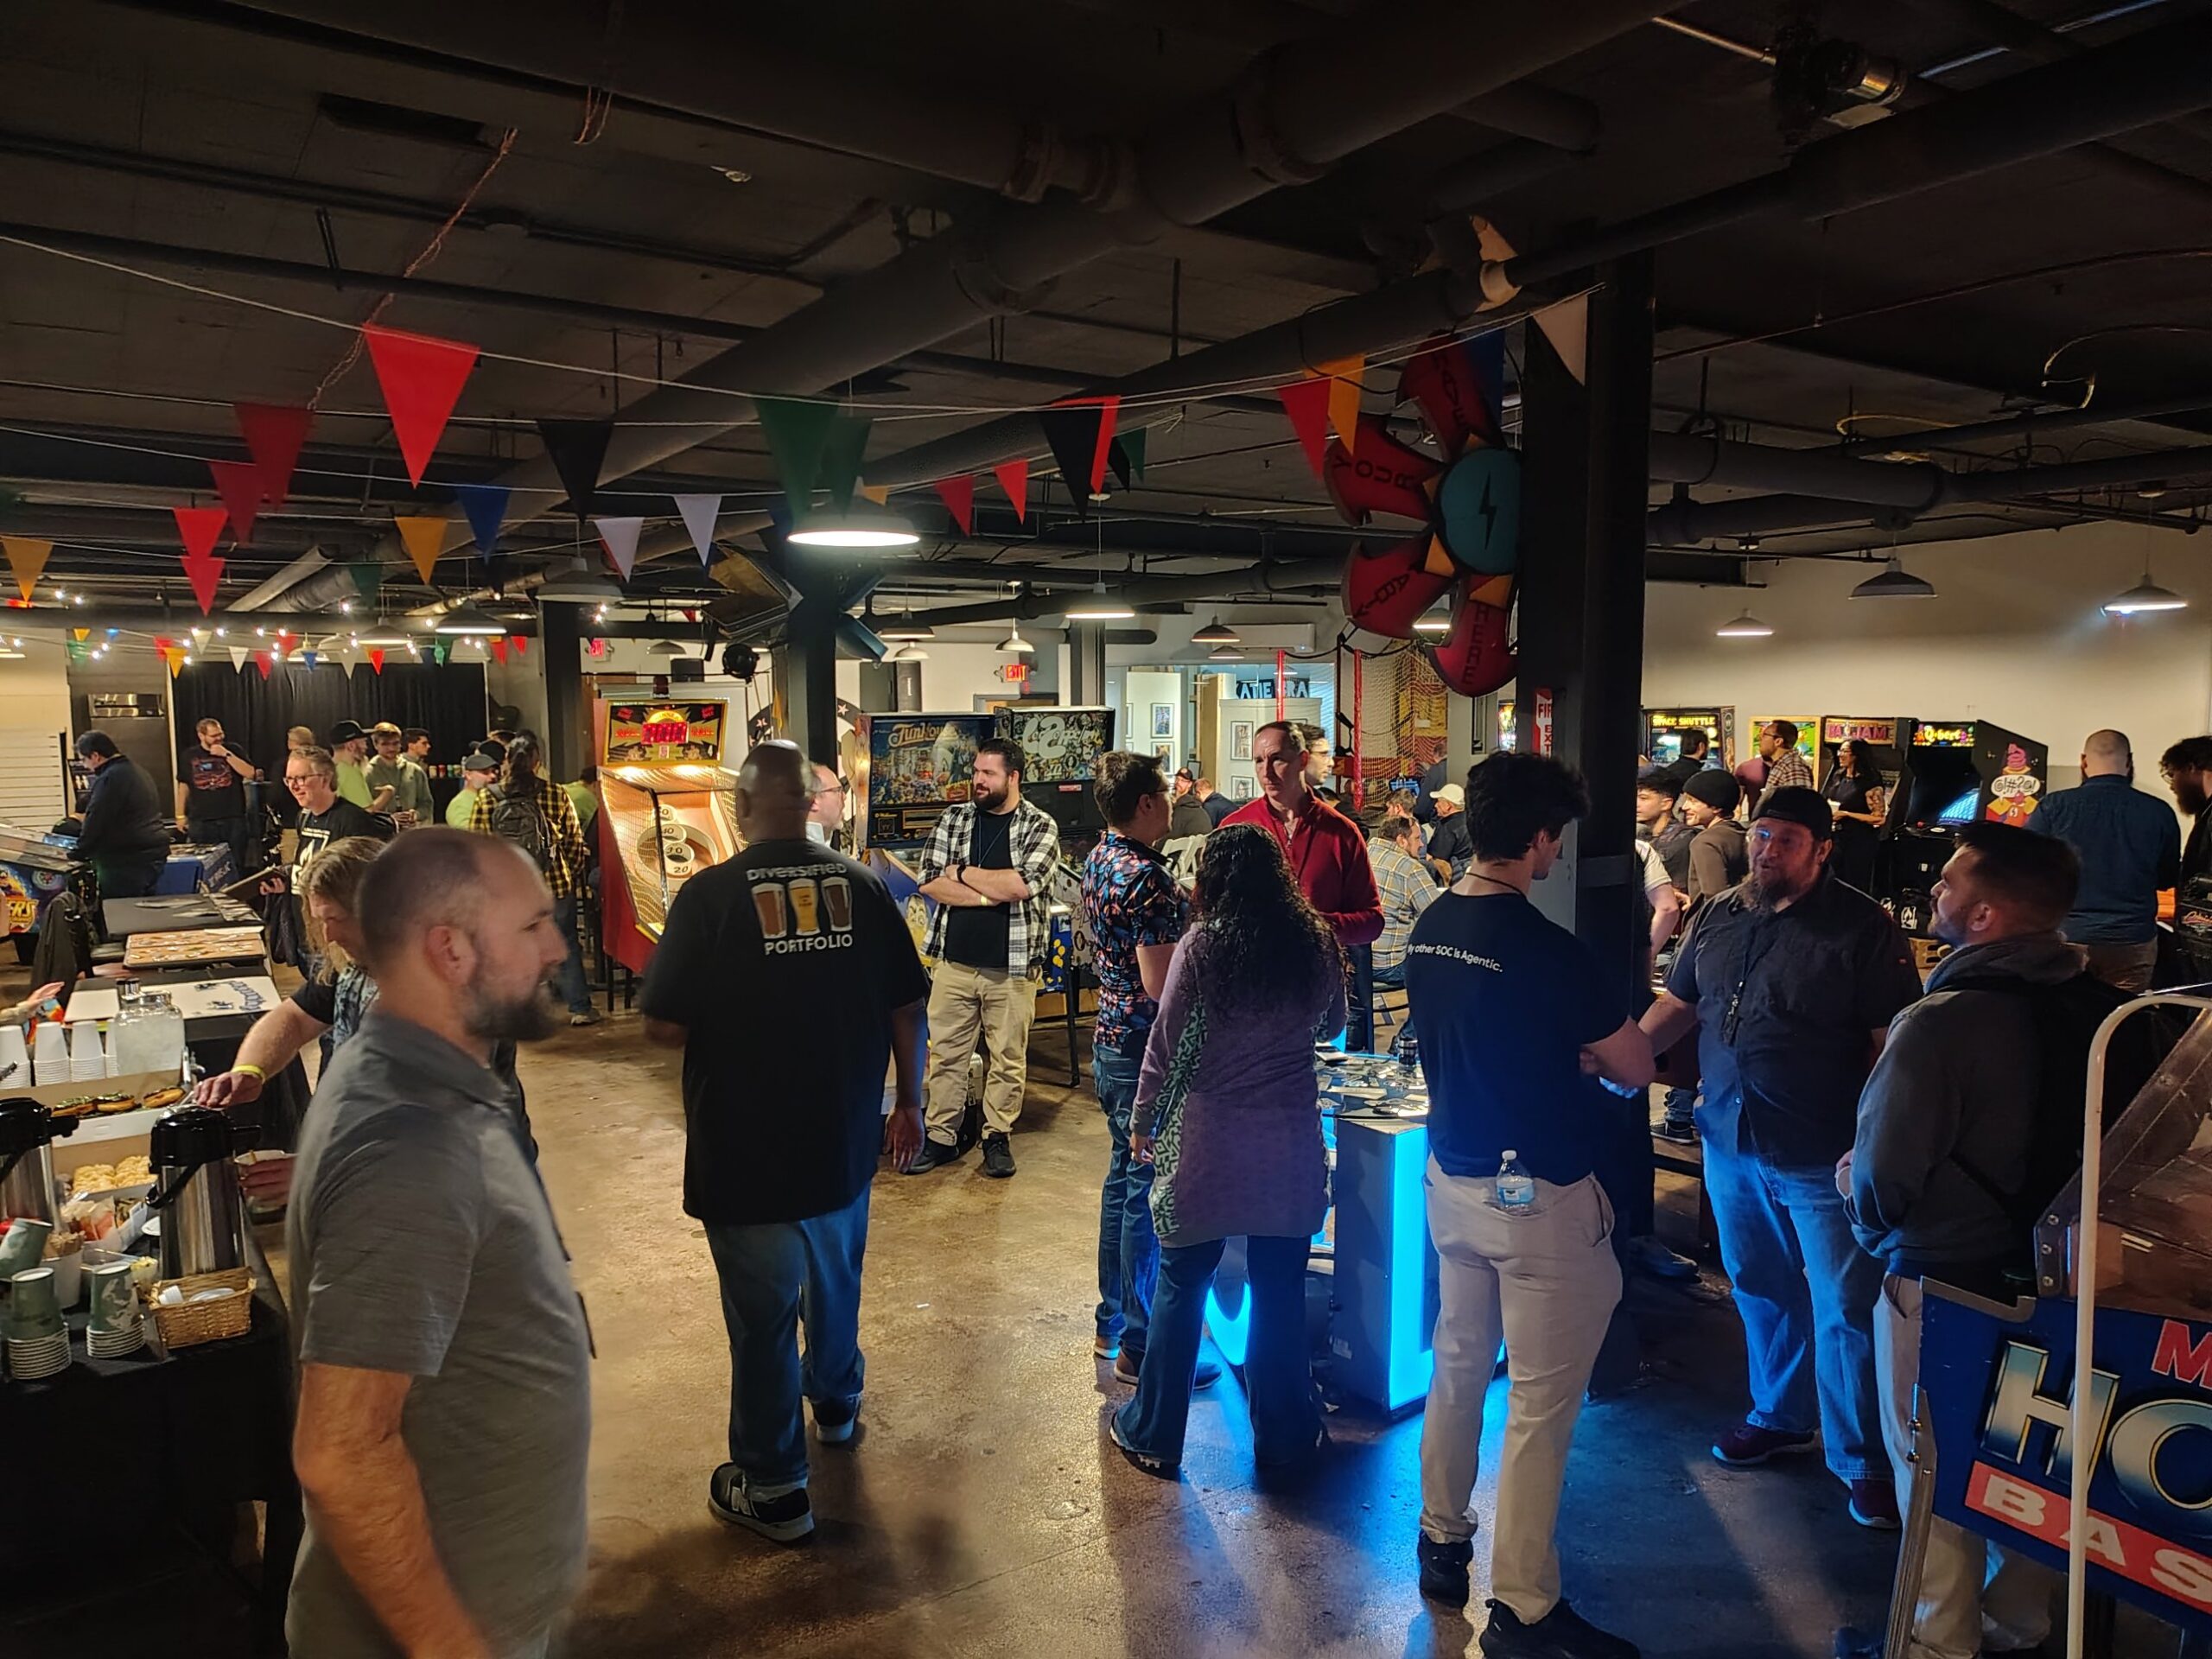
Burning River Cyber Con distinguishes itself from larger, vendor driven trade shows through its practitioner first format. The conference was founded as a place for offensive security professionals to talk shop and leave with actionable knowledge, with an emphasis on techniques that are proven in live engagements rather than theory or marketing. The 2026 agenda continued that approach with a single track of focused sessions, giving every attendee access to every talk and encouraging conversation between presentations.
2026 Session Program
The published schedule featured nine sessions spanning exploit intelligence, artificial intelligence security, password cracking, enterprise infrastructure attacks, threat detection and industrial control systems.
| Time | Session | Presenter |
|---|---|---|
| 9:00 AM | Doors open and registration | |
| 9:30 AM | Fresh Exploits, Weekly: Inside VulnCheck’s Initial Access Community | Spencer McIntyre |
| 10:00 AM | Have Your AI Hack the AI: Automated LLM Red Teaming with Augustus | AJ Hammond |
| 11:00 AM | Password Cracking on Modern FPGAs | Nic Losby |
| 11:45 AM | Lunch | |
| 12:45 PM | Just When I Thought I Was Out… SCCM Pulls Me Back In | Garrett Foster |
| 1:45 PM | Less Noise, More Nemesis: AI and Statistical Funnels for Threat Detection | Mike Pinch and Greg Stachura |
| 2:45 PM | Turning Everything Into a SOCKS Proxy | Skyler Knecht and Kevin Clark |
| 3:45 PM | MLOKit: MLOps Attack Toolkit | Brett Hawkins |
| 4:45 PM | You Can’t Nessus a Blast Furnace | Vina Ta |
| 5:00 PM | After party reception at Terrestrial Brewing Company |
Key Themes From the Program
Artificial Intelligence as Both Target and Tool
Three sessions addressed artificial intelligence directly. Presenters examined automated red teaming of large language models, attack paths against machine learning operations (MLOps) pipelines, and the use of AI and statistical methods to reduce alert noise in security operations. For organizations adopting AI tools, the message was clear: these systems introduce new attack surfaces and should be assessed with the same rigor as any other business critical platform.
Enterprise Infrastructure Remains a Priority Target
Sessions on Microsoft System Center Configuration Manager (SCCM) and network pivoting through SOCKS proxies highlighted how attackers continue to abuse trusted management tools and internal network paths once they gain an initial foothold. These are practical reminders that configuration hygiene and internal segmentation matter as much as perimeter defenses.
Exploit Intelligence and Credential Security
The opening session focused on how quickly newly published exploits are weaponized, while the FPGA password cracking presentation illustrated the growing speed of modern hardware against weak or reused passwords. Together they reinforced the value of rapid patching, strong password policies and multifactor authentication.
Protecting the Industrial Heartland
The closing talk, “You Can’t Nessus a Blast Furnace,” spoke directly to the region’s manufacturing and industrial base. Operational technology environments such as steel production, utilities and manufacturing lines cannot always be scanned or patched like office networks, and they require specialized, carefully planned security approaches. That topic carries particular weight in the Mahoning Valley, where industry remains central to the local economy.
Partners and Supporters
The 2026 conference was supported by the North East Ohio Cybersecurity Consortium (NEOCC), Northern Ohio InfraGard, NXGN, NavPoint Alpha, Exaforce and KT Wellington, with additional support from Nomad Security. Their involvement reflects a growing regional network of organizations committed to strengthening cyber resilience across Northeast Ohio.
Why It Matters for Youngstown and the Mahoning Valley
Small and midsize businesses across Youngstown, Boardman, Austintown, Canfield, Warren and surrounding communities face many of the same threats discussed in Cleveland: ransomware, credential theft, phishing and attacks on the systems that keep operations running. Regional events such as Burning River Cyber Con give local professionals direct access to current research, practical defensive guidance and a network of peers who understand the realities of doing business in Northeast Ohio.
Recommended next steps for local organizations include:
- Reviewing patch management practices so that newly disclosed vulnerabilities are addressed quickly
- Enforcing strong, unique passwords and multifactor authentication on every business account
- Inventorying AI tools in use and evaluating how they access company data
- Assessing internal network segmentation and administrative tool permissions
- Engaging qualified security professionals for periodic testing and assessment
Looking Ahead
With two successful editions completed, Burning River Cyber Con has established itself as a dedicated home for practical, technical security discussion in the Rust Belt. Professionals interested in future events, speaking opportunities or sponsorship can follow updates at BurningRiverCyberCon.com or contact the organizers at burningrivercon@proton.me.
For more local events, organizations and services across the Mahoning Valley, explore the Youngstown Local Index directory.